2022 Information Risk Insights Study
The 2022 Information Risk Insights Study uses a decade of public incident and loss records to estimate how often cyber events happen and what they cost. The typical reported loss is $266K, but the top 5% of events cost $52M or more. The analysis covers 77,000 cyber events affecting 35,000 organizations from 2012 to 2021.
Incidents are becoming more common, but one widely held belief doesn’t survive the data: inflation-adjusted median losses show no significant trend up or down over 20 years, even as the most extreme losses have crept higher. Size cuts two ways. The largest enterprises are far more likely to face several incidents in a year, while small businesses take most of the losses that are large relative to their revenue. Sector rankings also change depending on the measure, since the industries with the most incidents on record aren’t the ones most likely to have one in a given year. For risk analysts, the case is for probabilistic estimates matched to an organization’s size and sector rather than single averages.
The full report publishes frequency and loss model parameters (with upper and lower bounds), likelihood tables by revenue tier, loss statistics by sector and size, and a records-to-losses table to replace flat per-record costs. It adds a loss exceedance curve, a tail value-at-risk analysis and the top MITRE ATT&CK initial access techniques by sector.
Key Findings
- 44% More Incidents per Month: The typical number of publicly reported events per month rose from 496 in 2012 to 2013 to 718 in 2020 to 2021.
- $266K Typical, $52M Extreme: The typical reported loss from a cyber event is $266K, while the top 5% of loss events reach $52M or more.
- No Rise in Median Losses: Inflation-adjusted median losses show no statistically significant trend up or down over 20 years, though extreme losses have trended up.
- 32x for Three or More: Firms with over $100B in revenue are 32 times as likely as $10M to $100M firms to have three or more incidents a year.
- 89% of Severe Hits on SMBs: Small businesses were the primary victim in 89% of loss events that exceeded 10% of annual revenue.
- System Intrusions Lead: System intrusions account for about half of all events (49.6%) and 60% of recorded losses over the decade.
- Credentials and Phishing First: Valid accounts, phishing and exploited public-facing applications are the three most common ATT&CK initial access techniques across incidents.
Independent analysis by Cyentia Institute, with support from CISA and Lawrence Livermore National Laboratory, of 77,000 cyber events affecting 35,000 organizations from 2012 to 2021 in Advisen’s Cyber Loss Data.
Key Risk Insight
Most organizations won’t have a publicly known incident in a given year, but the odds and the relative cost vary sharply with size and sector. Plan for the unlikely, expensive outcome using estimates matched to the organization, not industry averages or cost-per-record shortcuts.
Cite this report: Cyentia Institute (2022). 2022 Information Risk Insights Study. https://www.cyentia.com/publication/iris-2022/
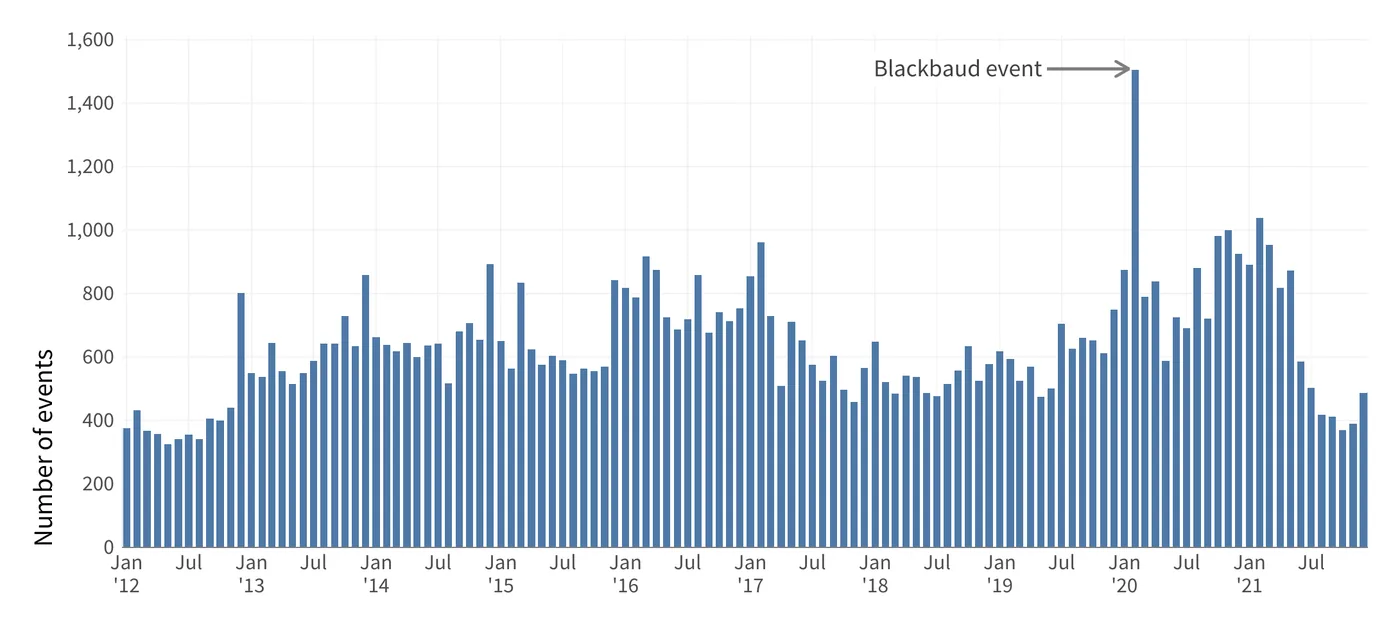
Figure 1: Number of publicly reported cyber loss events each month from 2012 to 2021. The typical monthly count rose about 44% between 2012 to 2013 and 2020 to 2021; the recurring year-end spikes come from events that can only be dated to a year. 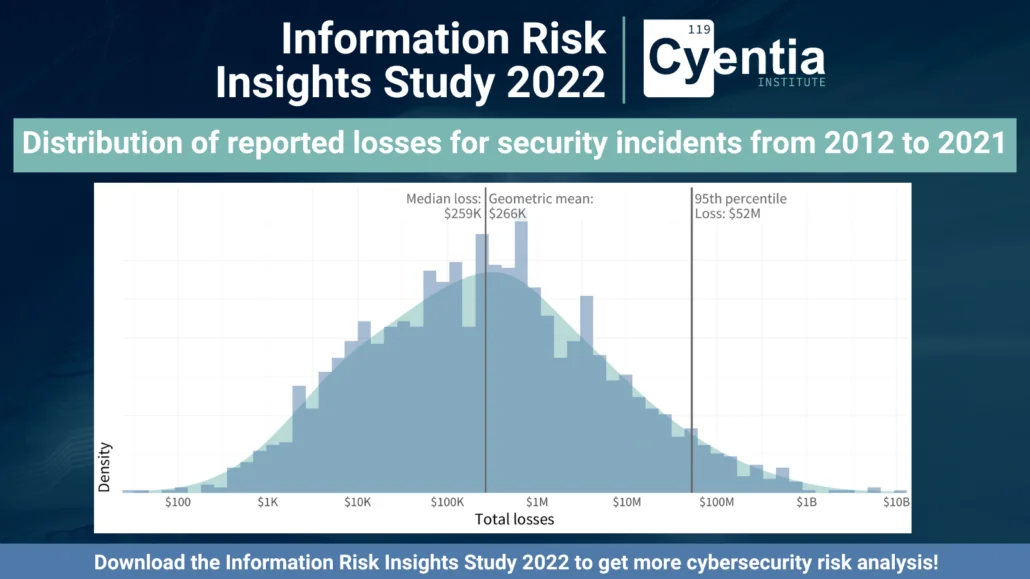
Distribution of reported losses for security incidents from 2012 to 2021 (IRIS 2022 infographic, Figure 6). The typical loss is about $266K, while the top 5% of events cost $52M or more. 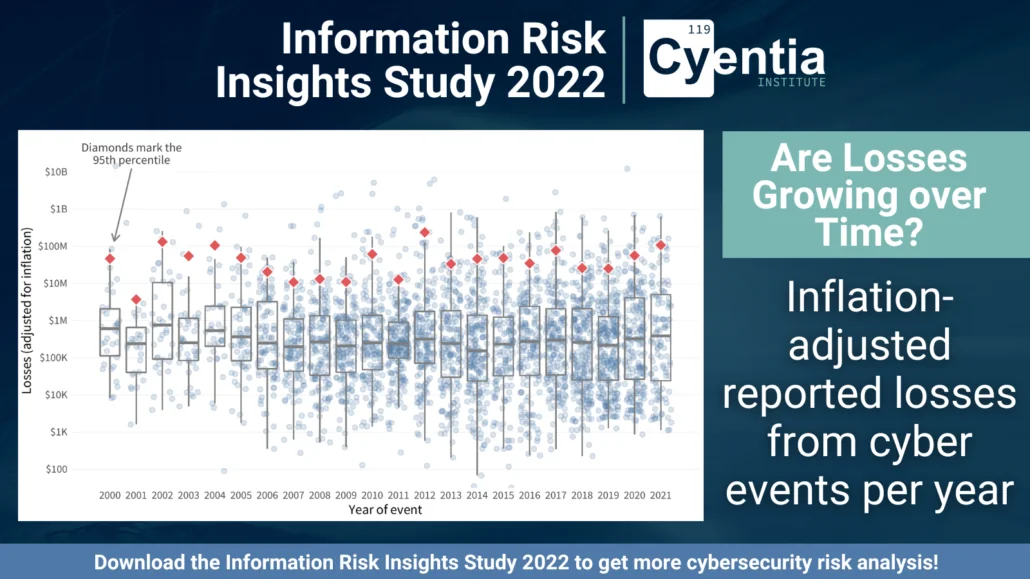
Inflation-adjusted reported losses from cyber events per year (IRIS 2022 infographic, Figure 9). Median losses show no significant trend up or down over 20 years, though the most extreme losses have crept higher. 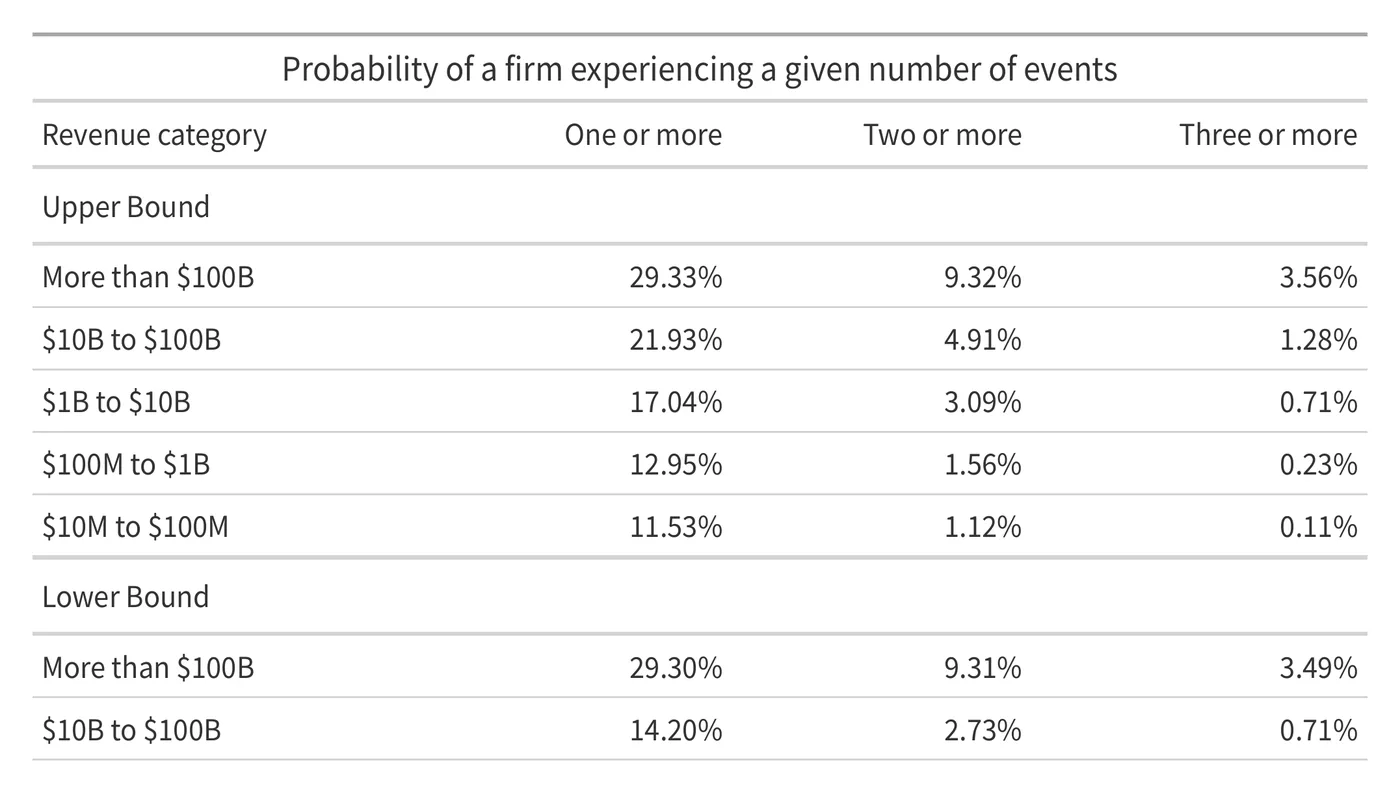
Table 2: Quick reference for loss event frequency estimates. The largest firms are about 2.5 times as likely as $10M to $100M firms to have at least one event a year, and 32 times as likely to have three or more. 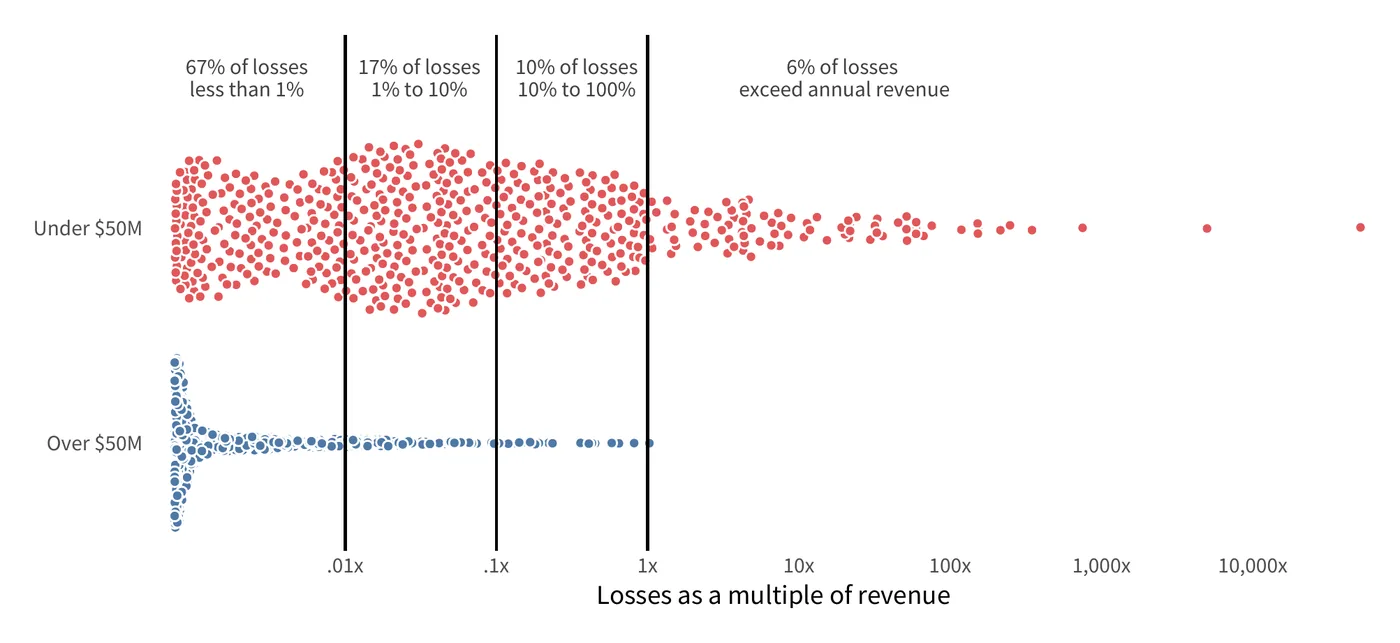
Figure 8: Distribution of event losses as a percentage of annual revenue. Two-thirds of incidents cost less than 1% of revenue, but 6% exceed the victim’s annual revenue, and small businesses account for almost all of the losses that are large relative to revenue. 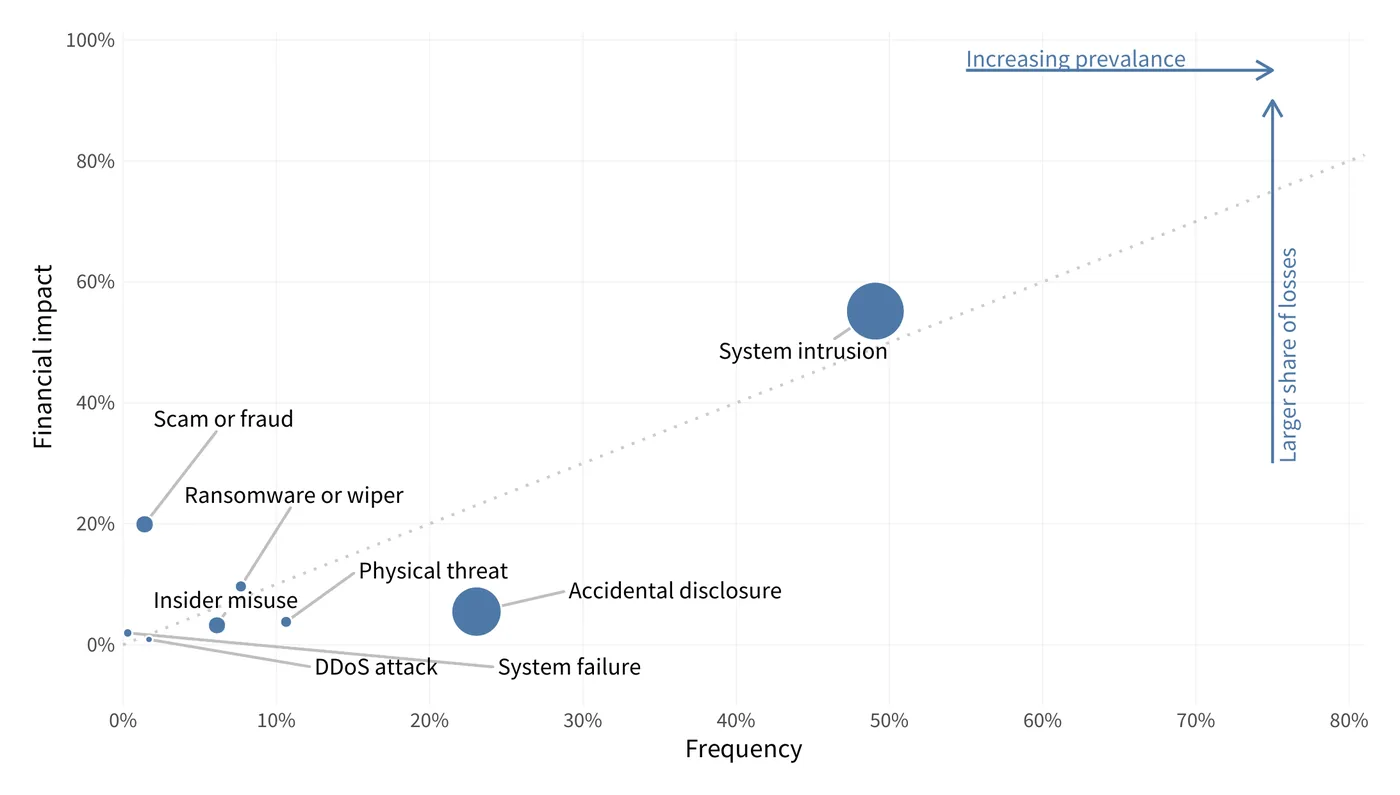
Figure 15: Relative frequency and losses associated with common incident patterns. System intrusions are the riskiest pattern by a wide margin, accounting for about half of all events and 60% of recorded losses over the decade. 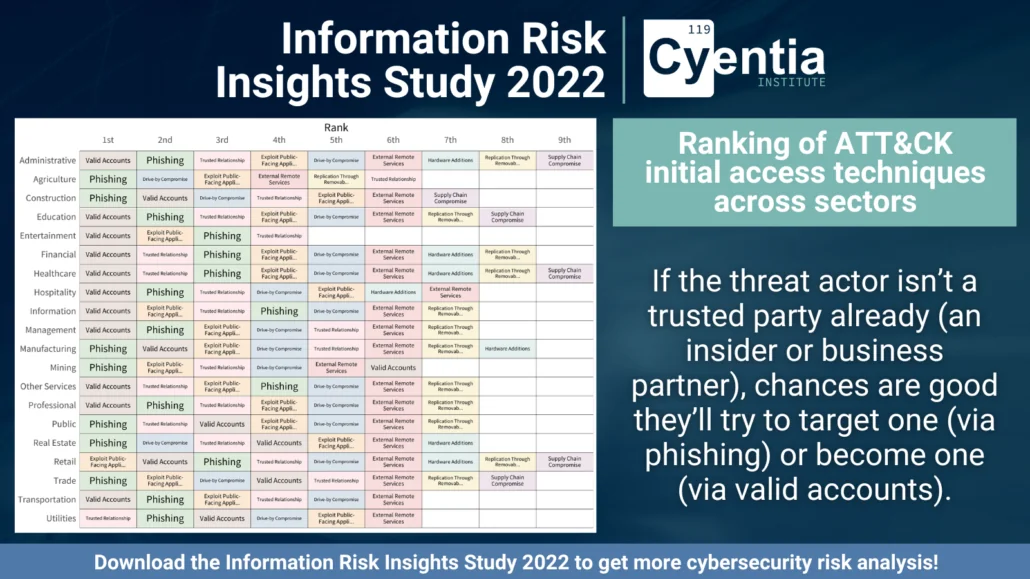
Ranking of ATT&CK initial access techniques across sectors (IRIS 2022 infographic, Figure 16). Valid accounts, phishing and exploited public-facing applications are the most common ways in, whatever the sector. 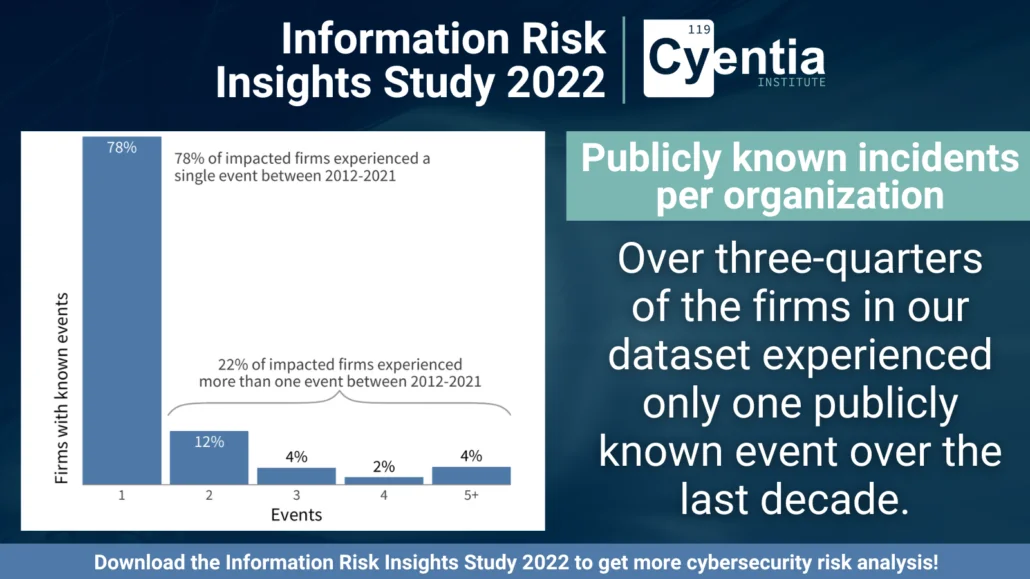
Publicly known incidents per organization (IRIS 2022 infographic). Over three-quarters of firms in the dataset had only one publicly known event over the decade. 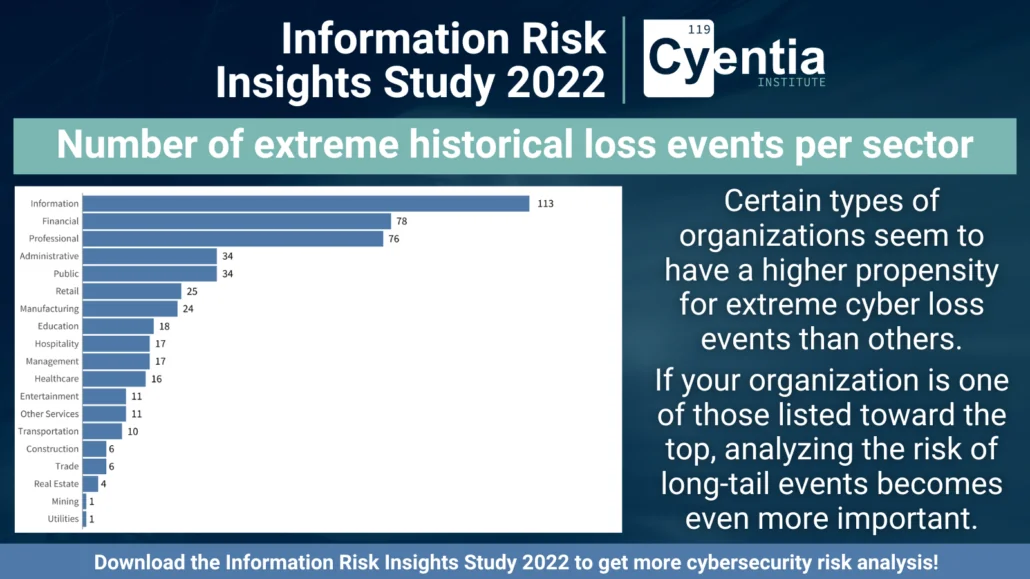
Number of extreme historical loss events per sector (IRIS 2022 infographic, Figure 14). Some sectors produce far more extreme losses than others, which makes tail risk analysis more important for them. 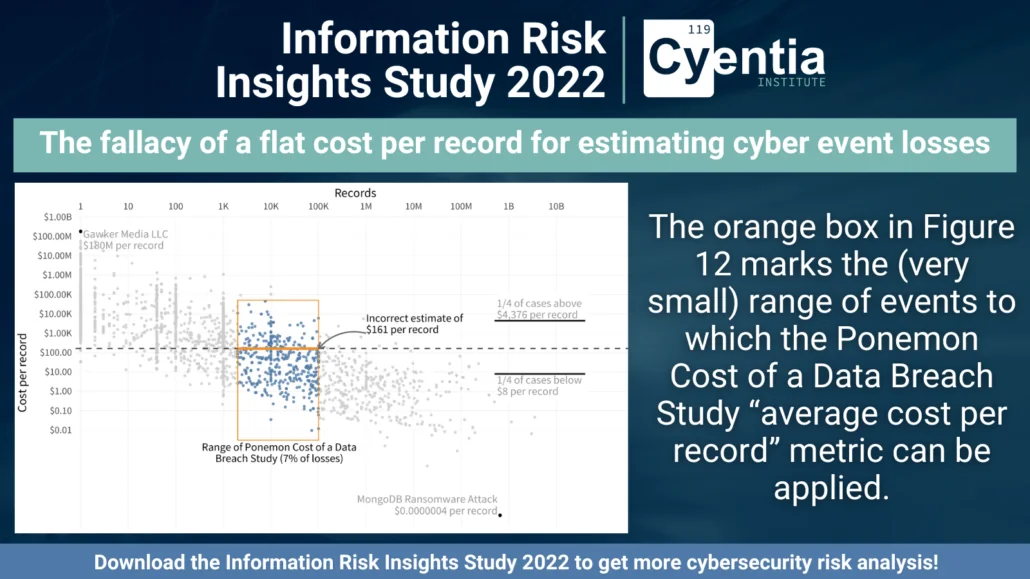
The fallacy of a flat cost per record for estimating cyber event losses (IRIS 2022 infographic, Figure 12). A single cost-per-record figure fits only a small slice of real events, so it misjudges most losses badly. 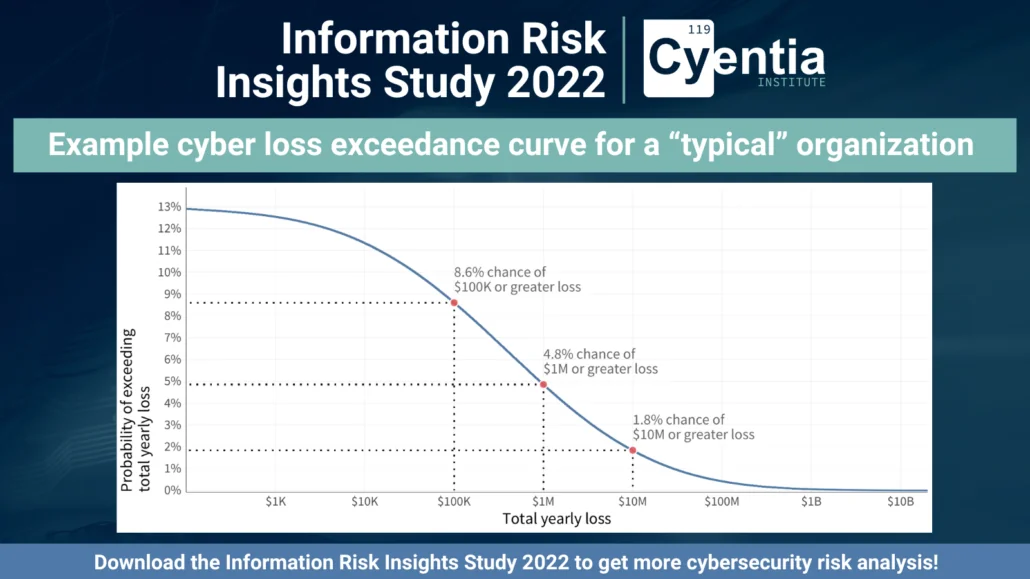
Example cyber loss exceedance curve for a “typical” organization (IRIS 2022 infographic, Figure 13). Most organizations won’t see a publicly known loss in a given year, but the curve shows how likely the expensive outcomes are.
Get exclusive content, sector-specific updates, and expert commentary
Testimonials
Need an IRIS Focused on Your Organization?
That’s exactly what our Retina risk intelligence service provides. You get a report on key cyber risk factors for your peer group, along with monthly data and analysis to monitor prevailing trends.