
Information Risk Insights Study: Tsunami Edition, 2021
The IRIS Tsunami follows 50 of the largest multi-party cyber incidents to see what caused them and how the damage spread to other organizations. The median event cost $90M and pulled in 31 secondary organizations, and the largest reached 800.
Multi-party incidents are often discussed as a vendor-risk problem, and the data supports that with a twist. Most of these events began with a system intrusion at the central firm, but ransomware, though less common, carries the largest share of losses. Stolen and misused credentials show up again and again, and insiders and third parties were far more often the vector than the villain, contributing to 34 of the 50 events. The damage spread most often through data held by an aggregator, while compromises of the software supply chain caused the biggest losses and the most downstream victims. State-affiliated actors were behind a minority of events but most of the recorded losses. For third-party risk teams, the lesson is to look past whether a partner is trustworthy and ask what access and data it holds.
The full report sizes these events by organizations affected, records compromised and losses, and breaks them down by incident pattern, MITRE ATT&CK initial access technique and VERIS threat action. It describes six ways ripples propagate, profiles the threat actors and the sectors that generate these events, and includes detailed data tables.
Key Findings
- $90M Median Cost: The median recorded loss for these 50 multi-party events is $90M, versus about $200K for a typical incident.
- 31 Firms per Event: The median event impacted 31 secondary organizations, and the largest reached as many as 800.
- 44% of Losses From Ransomware: Ransomware was a distant second to system intrusion in frequency but accounts for 44% of recorded losses.
- Credentials in Half: Credential attacks played a part in 25 of the 50 events, which together account for 68% of recorded losses.
- $7.4B via Supply Chain Compromise: Supply chain compromises produced the largest share of losses and the most secondary victims of any propagation method.
- State Actors, $10B+: State-affiliated groups were behind one in five events but over $10 billion (58%) of recorded losses.
- 99% Involve Trusted Parties: Insiders or third parties caused or contributed to 34 of the 50 events, which account for 99% of recorded losses.

Independent analysis by Cyentia Institute, with support from CyberGRX, Interos and RiskRecon, of the 50 largest multi-party cyber incidents in Advisen’s Cyber Loss Data, each researched from public sources.
Key Risk Insight
The costliest multi-party incidents usually spread through trusted access or shared data rather than malicious partners. Third-party risk programs should focus on what access and data each partner holds, not only on whether the partner itself is secure.
Cite this report: Cyentia Institute (2021). Information Risk Insights Study: Tsunami Edition, 2021. https://www.cyentia.com/publication/iris-tsunami/
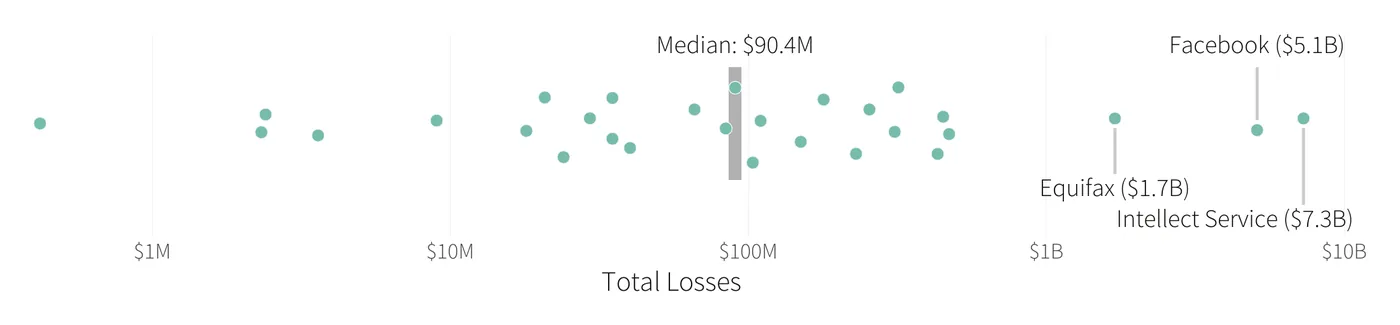
Figure 3: Total recorded financial losses for extreme multi-party cyber incidents. The median event cost $90M, against about $200K for a typical incident. 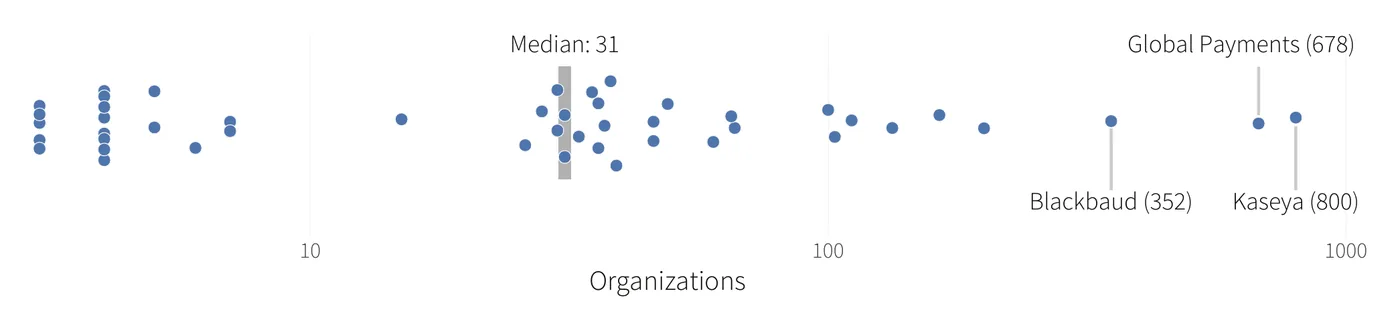
Figure 1: Number of secondary firms impacted by extreme multi-party cyber incidents. The median event pulled in 31 other organizations, and one in four reached 55 or more. 
Figure 6: Basic incident patterns among extreme multi-party cyber incidents. Most of these events began with a system intrusion, but ransomware carries the largest share of losses. 
Table 1: All threat actions observed among extreme multi-party cyber incidents. Credential attacks played a part in half of these events and two-thirds of recorded losses, which often makes insiders and partners the vector rather than the villain. 
Figure 8: Downstream propagation methods in extreme multi-party cyber incidents. Damage spread most often through aggregated data, while supply chain compromises caused the biggest losses and the most secondary victims. 
Figures 9 and 10: Threat actor categories, and organized criminal vs. state-affiliated actors, in extreme multi-party cyber incidents. State-affiliated groups were behind one in five events but over $10B of recorded losses; insiders and third parties rarely act as the attacker but often serve as the way in.
Get exclusive content, sector-specific updates, and expert commentary
Testimonials
Need an IRIS Focused on Your Organization?
That’s exactly what our Retina risk intelligence service provides. You get a report on key cyber risk factors for your peer group, along with monthly data and analysis to monitor prevailing trends.